
















Privacy and data hygiene aren't optional, even for the smallest social media businesses. As a solo social manager you handle client accounts, audience lists, DMs, campaign exports and creative files. Each one is a potential liability if it's left untracked, shared carelessly, or kept longer than it needs to be. This checklist is meant to be practical and quick. It's for people already juggling content, edits and approvals. The aim isn't to become a security expert overnight. It's to pick up a handful of repeatable habits that make data risk manageable and slot neatly into the client workflows you already have.
Read this guide once to get the full picture, then use the short action items at the end of each section to make progress. The recommendations work with any tool. Use the password manager you already like, the encrypted cloud drive you already trust, and the scheduling app that runs your posting. The job is to make those tools work in a way that protects client data and keeps your work audit-ready. If something feels time-consuming, split it into two 30-minute sessions across the week. Small, steady improvements beat one heroic cleanup that never gets repeated.
This guide covers six practical areas: inventory, access control, data minimisation and retention, third-party integrations, message handling and audience data, and basic backups and incident response. Each section explains why it matters and gives you exact actions you can tick off today. Follow through and your client contracts and onboarding materials will go from vague to professional with just a few edits.
1. Know what you hold and why
Inventory is the most underrated privacy habit. Too many solo managers assume they'll remember what files and exports exist. Memory fails. Old CSVs pile up, forgotten accounts keep their shared access, and copies of chat logs multiply across devices. A clear inventory turns vague worry into specific tasks you can fix.
Start small. Create a single inventory file or a secure note for each client. For every asset, record: the platform or resource name, the type of data (credentials, audience export, screenshot, analytics CSV), who provided it, why you keep it, where it's stored right now, and how long you plan to keep it. Use columns like: asset, data type, storage location, retention date, who can access, last reviewed. The goal is to answer two questions quickly for any client: what is stored, and when will it be deleted.
Make the inventory realistic. If you have 20 clients, a single sheet with one line per active asset is enough. Don't try to document every draft in your working folder. Focus on exports, shared credentials, audience lists, and any file that contains personal data. If a file only holds creative JPEGs with no names or emails in the filenames, mark it as low sensitivity. If it contains emails, phone numbers or private messages, mark it as high sensitivity and give it a deletion date.
Practical tips to keep the inventory useful: add a short note to each entry explaining why you keep the file and what happens next. For example: "Campaign export for June ads - keep until 2027-01-01 then delete" or "Influencer contact list - used for Q3 outreach - delete after campaign ends." Add a "last reviewed" column and set a calendar reminder to audit the inventory every quarter.
Why this saves time: when a client asks for a data export or asks you to delete something for privacy reasons, you won't have to hunt through folders. You'll also spot files you can delete today to cut risk. A five-minute inventory update often clears out the riskiest items and gives clients confidence that you know where their data lives.
Common traps and how to avoid them: don't use plain text notes or unsynced spreadsheets on your laptop for sensitive inventories. Use a secure note inside your password manager instead, or an encrypted cloud document with limited sharing. Avoid putting actual passwords in the inventory; store only metadata and links pointing to the password manager entry.
Immediate actions: create the inventory file and add every export and account credential you've touched in the last 90 days. Flag anything with emails or phone numbers as high sensitivity and add a deletion or archive date.
Deepening the inventory so it's actually useful
If the inventory stops at filenames, it'll only be marginally helpful. Add a few short fields that make the list actionable at a glance. A "business purpose" column explains why the data exists. A "next step" column says whether the file should be deleted, moved to encrypted storage, or kept until a specific date. A "risk level" column helps you triage: low, medium or high. These tiny annotations make quarterly audits fast, because you can filter the sheet for "high" items and deal with them first.
Add a simple tagging system. Tag items as EXPORT, CREDENTIAL, TRANSCRIPT, IMAGE or ANALYTICS. Tags let you run quick queries in the spreadsheet or sort by type. For example, sorting by EXPORT shows you every audience file you might purge after a campaign. Sorting by CREDENTIAL shows you who still has access and whether any credentials are shared insecurely.
Link inventory entries to the actual secure storage. Instead of copying passwords into the sheet, include a password manager link or a short note pointing to the manager entry. For files stored in cloud folders, add a path or a short link and note whether the folder is encrypted. This avoids risky duplication of secrets while keeping the inventory useful.
Who should own the inventory
If you manage multiple clients, make the inventory your responsibility but share a read-only summary with each client. The summary can list what types of data you store for them and the next scheduled deletion dates. This builds trust and cuts down on questions later. For clients who insist on full control, give them a template and ask them to keep an owner copy. Your copy focuses on the operational items you need to do your job.
When to tidy up
Set a short ritual: spend 15 minutes each Friday updating the inventory with new exports, new credentials and any changes in access. This small, regular habit saves you from a painful marathon cleanup later. Every quarter, run a deeper 60-minute review to delete old exports, rotate any shared credentials and confirm retention dates.
Immediate checklist for the inventory deepening
- Add a business purpose and next step column to the inventory
- Tag each item with a simple type label (EXPORT, CREDENTIAL, TRANSCRIPT, IMAGE, ANALYTICS)
- Add password manager links instead of raw credentials
- Set a weekly 15-minute update and a quarterly 60-minute audit
These steps turn a list of filenames into an operational control centre you can actually use during client requests and audits.
2. Lock down access and credentials
Access mistakes are the low-hanging fruit of account takeovers. Strong passwords and two-factor authentication are the standard fixes, but a few extra habits matter more for solo operators: put everything into a password manager, favour platform-level roles over shared credentials, and have a recovery plan written down.
Use generated, unique passwords and never paste them into chat. Share access through your password manager, or invite collaborators through platform roles where you can. If you must use a shared credential, rotate it straight after the work is done and log the rotation in your inventory. When you give contractors temporary access, create temporary seats or throwaway accounts and revoke them as soon as the job is finished.
Two-factor authentication should use authenticator apps or hardware keys where possible. SMS is acceptable, but avoid it for high-risk accounts. Add a note to your onboarding document describing the recovery process, who owns the recovery email, and how to handle account recovery if a client loses access.
Extra steps for higher-risk clients: keep a secure copy of recovery codes in your password manager and mark them as accessible only to the client owner by default. If a client has several team members, insist they keep a central admin seat tied to a business email rather than a personal account. This stops a single departing contractor from becoming the recovery owner.
Immediate actions: add every active client account to your password manager, turn on 2FA where it's available, and note recovery contacts in the inventory. Set a six-month reminder to rotate critical passwords and review who has access.
3. Minimise data collection and set retention rules
Collect less and keep less. That's the simplest privacy rule there is. Before you export an audience, ask whether you'll use the full dataset this month or whether a filtered subset will do. Before you download DMs, confirm you need the export for a legal or reporting reason, not just a casual backup.
Create retention categories that are easy to follow. For example: transient logs (keep 30 days), campaign exports (keep 90 to 180 days), client-approved creative assets (keep one year), legal evidence (keep until the client tells you to delete it). Use clear, predictable windows so you and your clients can plan. When you keep files longer, log the reason in the inventory so later reviewers understand the business purpose.
Automate deletion where you can. Some cloud providers and scheduling tools offer automatic retention or trash expiry. Use those features for exports and temporary logs. If automation isn't available, set calendar reminders tied to the inventory entries so files get deleted on schedule.
Labelling helps a lot. Put retention dates in filenames like "clientname_campaign_exports_2026-06_Delete_2027-06-01.csv". That makes cleanup simple and takes the guesswork out of it.
Immediate actions: find exports from the last six months you can delete, set retention dates for the rest, and turn on automatic trash retention on your cloud storage. Talk clients through the retention policy during onboarding so they can flag anything that needs to be kept longer.
4. Vet and limit third-party tools and integrations
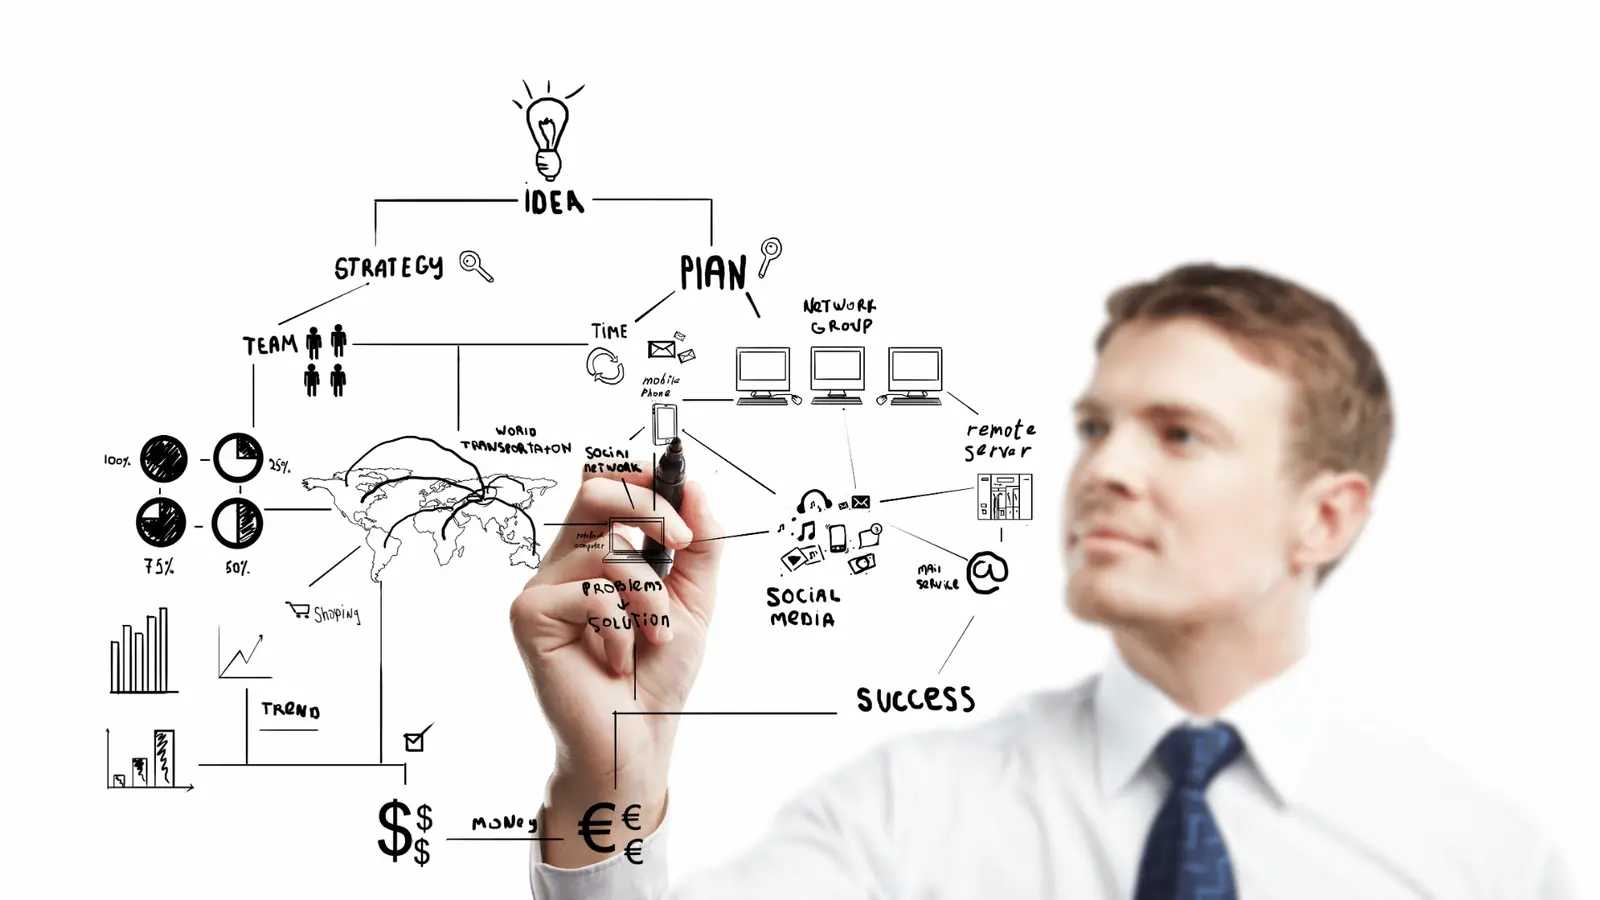
Third-party tools are where unnoticed risk builds up fast. You might sign up for a new analytics dashboard or AI caption tool and grant it broad permission because you need one feature. Later, that tool might hold on to exports or suffer a data breach. The easiest defence is a short vendor checklist you run every time you add a tool.
Vendor checklist: what data does the tool ask for, can you limit the scope, is data stored outside the region you and the client need, does the vendor have a clear privacy policy, how long do they keep exports, and can you revoke access without changing account passwords? Favour OAuth-based connections, because they let you revoke access cleanly. Avoid tools that ask for full login credentials.
Record the answers in your inventory. For each tool, write down the permission scope and a short line on the risk level and how you'll mitigate it. For tools you use temporarily, create throwaway accounts or limit them to non-production assets. For long-running integrations, keep an eye on their notification emails for policy changes and schedule a quarterly re-check.
Browser extensions are a special case. They can read page content and sometimes send data out. Use a separate browser profile for work and limit extensions to ones you trust. Keep automation and API keys in a secrets manager and don't paste them into scripts or shared documents.
Quick actions: review the authorised apps page on your key platforms this week and revoke anything suspicious. Add every connected tool to your inventory with its permission scope and a scheduled review date. For any tool that stores exports by default, find out how to delete those exports or limit retention.
Why this matters: a compromised third party can expose several client accounts at once. Limiting permissions and keeping a short, documented vendor list shrinks the blast radius and speeds up incident response.
5. Handle messages and audience data with care
Messages are often where sensitive data turns up unexpectedly. A DM might include an email, a phone number or a private image. Screenshots used for internal notes or reporting can accidentally include personal details in the filename or the image metadata. Treat every message as potentially sensitive and give it a default handling rule.
Default rule examples: never copy raw messages into public notes, never store phone numbers in open spreadsheets, always move transcripts with personal data into encrypted storage, and remove or blur personal data from screenshots before saving them in shared folders. If you export DMs for a client, do a redaction pass to remove or mask personal data that isn't needed for the business purpose.
Community management needs explicit rules. Decide in advance whether you'll keep member lists, whether you'll store message histories for moderation, and how long you'll keep records of rule violations. Put those policies in writing and add them to client agreements so everyone knows what to expect.
Logging practices: keep a short, dated log entry whenever you save a message export, noting why it was saved and when it should be deleted. This creates an audit trail and helps you remember the purpose months later. If a message export contains sensitive data, treat it as high sensitivity in your inventory and tag it for earlier deletion.
A few technical tips: strip EXIF metadata from images before storing them, rename image files to remove names or phone numbers, and use bulk redaction tools when you need to scrub lots of screenshots. If you use chatbots, set them up to avoid logging full messages or to anonymise identifiers by default.
Immediate actions: run a 90-day review of messages and support logs, delete anything unnecessary, move any required logs into encrypted storage, and add a message handling paragraph to your client onboarding explaining your retention windows and redaction process.
Why this matters: mishandled messages are a common complaint and a fast route to losing trust. Clear, written rules protect your client relationships and reduce legal risk.
Practical redaction workflows and tools
A manual redaction pass is slow and easy to get wrong. Use simple tools and clear steps to speed the job up. For text exports, open the file in a spreadsheet and replace or remove columns with emails and phone numbers. For screenshots, use a batch image editor or an online redaction tool that can blur or black out sensitive areas. When you have to share examples in reports, crop images to show only what's needed and add a short caption explaining why the screenshot is included.
For chat transcripts, use search to find the few lines you need and export only those lines rather than the whole conversation. If you share transcripts with a client, include a short note describing the redaction steps you took. That cuts down on back and forth and shows professionalism.
Automation and safety knobs
If you use chatbots or automated inboxes, add privacy controls. Set bots to drop identifiers or to write logs with hashed user IDs instead of raw emails. Some tools let you mask personal data automatically before it's stored. Turn those features on when you can. Also consider keeping logs in a separate, more secure storage location than your general creative assets. That separation reduces the chance that a simple folder sync exposes sensitive messages.
Handling community disputes and moderation evidence
When you keep logs for moderation or dispute resolution, treat those logs as temporary evidence. Keep them only as long as needed, archive them in encrypted storage, then delete them. Keep a short chain of custody note recording who accessed the evidence and when. This matters especially if you moderate groups that include minors or sensitive topics. Clear steps reduce personal liability and show clients you're handling moderation responsibly.
Immediate checklist for message handling
- Remove EXIF metadata from images before uploading
- Rename files to remove personal data from filenames
- Use batch redaction tools for screenshots and transcripts
- Set bots to anonymise or hash user identifiers
- Keep a short chain of custody log for moderation evidence
These rules make message handling a predictable part of your workflow rather than a source of stress.
6. Backups, incident response and audits
Assume errors happen and design for recovery. A simple backup and a short incident response checklist stop most crises from turning into disasters. The goal is speed and transparency: recover quickly and tell the client what happened, with no surprises.
Backups: keep a dated backup of approved creative and account exports in a secure, separate cloud location. Don't store backups in the same folder as working files. If you hand off accounts, include a dated export and a short note explaining what's included and why. For follower lists and settings that can't be backed up, keep a short change log with dates for major changes.
Incident response: write a one-page plan that covers common events. The plan should list who you notify first, how you revoke app access, the steps to rotate credentials, how to restore from backup, and templates for client communication. Keep the plan short and pinned in your project management tool so you can act quickly.
Audits: schedule a quarterly review that checks the inventory, confirms active access lists, reviews third-party tools, and verifies that retention rules are being applied. During the audit, rotate critical passwords, revoke stale app access and archive old exports. Keep a dated audit note in your inventory so you can show what you did and when.
Immediate actions: make a single backup of the last three months of approved assets, write the one-page incident response, and add a recurring calendar event for quarterly audits. If you ever need to respond to a breach, follow the plan, notify affected parties quickly, and document every action you took.
Conclusion
Privacy and data hygiene aren't a lot of extra work if they're built into the way you already run client work. Use the inventory as your control centre, lock down access, delete what you don't need, vet every tool, treat messages like sensitive data, and prepare a short backup and incident plan. Implement one section each week and you'll be in a much stronger position within a month.
Add the key action items to your onboarding pack and show clients the inventory summary. That simple transparency is often enough to turn privacy into a selling point rather than a liability.


 Google review
 Trustpilot review
 Product Hunt comment





